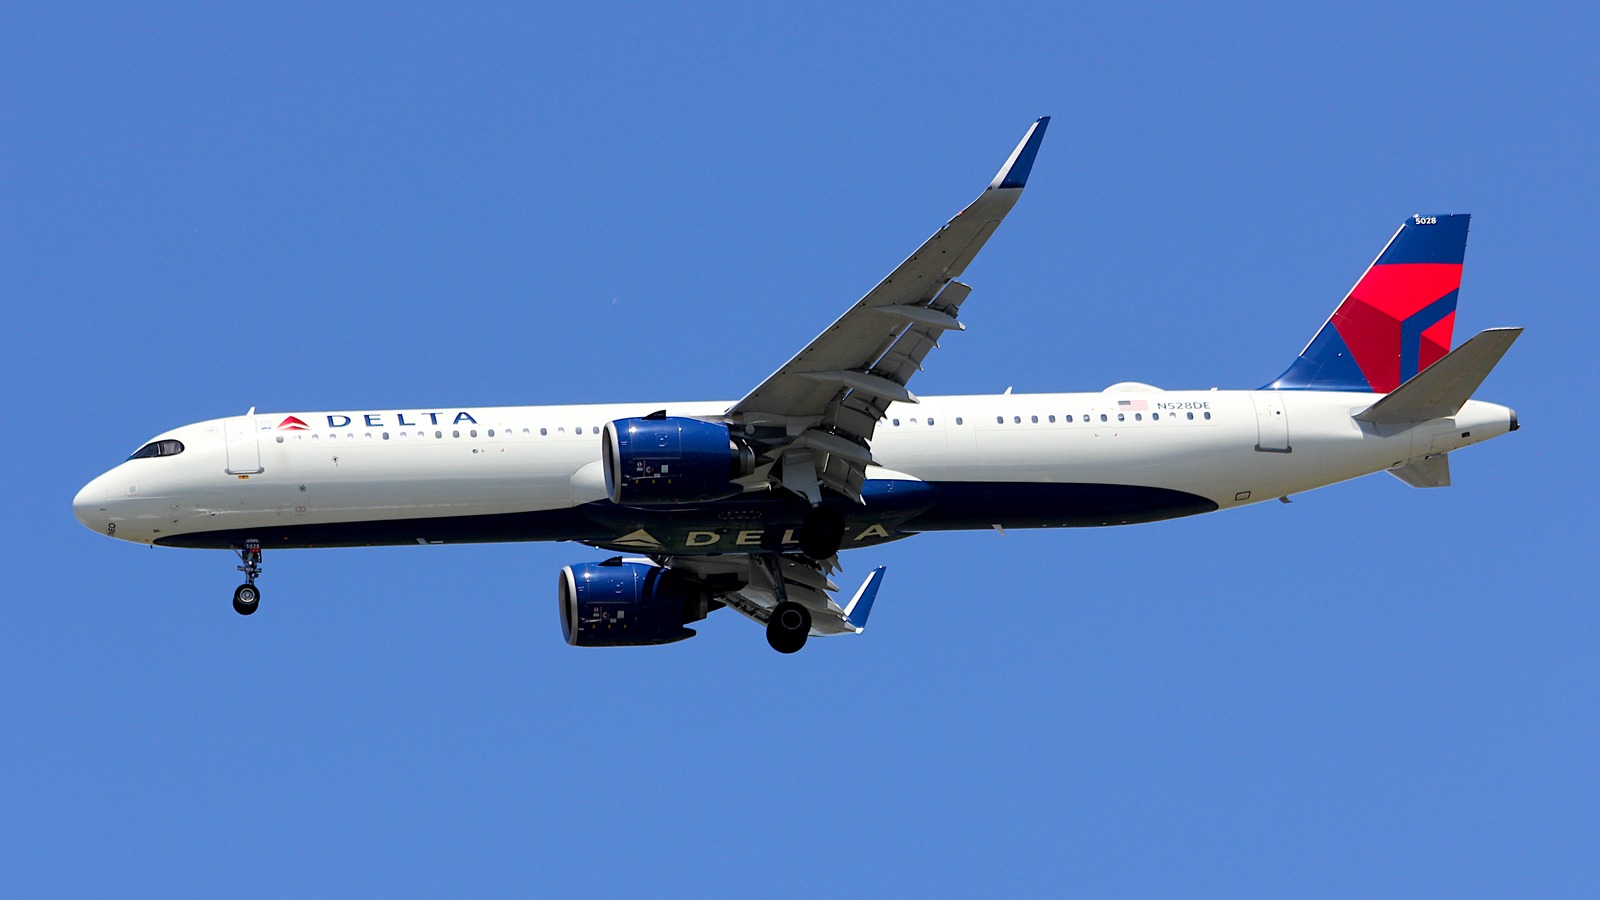
Delta Air Lines is investigating after an unauthorized Wi-Fi network appeared on Flight 591 from Las Vegas to Atlanta on Monday. The crew shut down the aircraft’s legitimate internet service for about 30 minutes while pilots alerted air traffic control, according to a Delta spokesperson and public radio traffic reviewed by TechCrunch.
The unusual part is what did not happen: Delta says the aircraft’s operating systems and real in-flight network were not compromised, and the safety of the flight was never in question. What remains unknown is who created the other network, what it was intended to do, and whether any passenger connected to it or entered information.
- The flight: Delta Flight 591 was traveling from Las Vegas to Atlanta on Monday.
- What appeared: Pilots reported a Wi-Fi network designed to resemble the aircraft’s legitimate connection.
- Crew response: Delta disabled its real onboard Wi-Fi for about 30 minutes while the situation was assessed.
- Safety status: Delta says no aircraft operating systems were affected and flight safety was not compromised.
- Traveler check: Delta tells passengers to select the network named DeltaWiFi.com and open DeltaWiFi.com in a browser.
What happened on Delta Flight 591
TechCrunch reported the incident after obtaining a statement from Delta spokesperson Morgan Durrant and reviewing publicly available air traffic control communications. The flight was operating from Harry Reid International Airport in Las Vegas to Delta’s Atlanta hub.
In the radio traffic, the pilots described a network that appeared to impersonate the aircraft’s real Wi-Fi. They did not identify a passenger, explain how the network was created, or report that anyone’s credentials were captured.
The pilots also mentioned that passengers had arrived from cybersecurity conferences held in Las Vegas. That timing is relevant context, but it is not proof that a conference attendee created the network, that the activity was malicious, or that a particular device was involved.
Delta’s response was deliberately broad. Durrant told TechCrunch that the airline was still gathering facts and planned to work with federal law enforcement and aviation regulators as it investigated.
Atlanta Police referred questions to federal authorities, while the Federal Aviation Administration told TechCrunch that it had not received a report about the incident at the time of publication. The FBI had not responded to the outlet, leaving the federal investigative status unresolved.
Why a look-alike network matters
A phone or laptop often displays only the network name, also called the SSID, before a traveler connects. Someone can create a separate access point with a familiar-looking name, but seeing that name does not prove the network belongs to the airline.
Security professionals often call that setup an evil twin when it is used to imitate a trusted connection. It can be created with ordinary hardware, yet TechCrunch stressed that the purpose of the network on Flight 591 is still unknown.
That distinction matters because a suspicious network and a hacked aircraft are not the same claim. Delta specifically said the airplane’s systems were unaffected, its legitimate in-flight network was not compromised, and the flight remained safe.
The practical risk for a passenger would be connecting to an impostor network and then trusting whatever page appeared. A convincing portal could ask for an email address, account credentials, payment details, or another piece of information, but there is no confirmed evidence that this happened on Flight 591.
The Federal Trade Commission’s public Wi-Fi guidance notes that most modern websites encrypt traffic, which makes ordinary public Wi-Fi safer than it once was. It still advises travelers to keep software updated, use strong passwords and two-factor authentication, and remember that a fake website may use encryption while still sending information to a scammer.
How Delta says passengers should connect
Delta’s official onboard Wi-Fi instructions give passengers a specific sequence. Put the device in airplane mode, turn Wi-Fi back on, choose the network named DeltaWiFi.com, and open DeltaWiFi.com in a browser if the sign-in page does not load automatically.
The airline also says travelers using a virtual private network should connect to the aircraft Wi-Fi before logging into the VPN. A VPN can protect traffic after a legitimate connection is established, but it cannot tell a traveler whether the first network selected belongs to Delta.
Passengers should pause when a network name differs from Delta’s published name, when several similar names appear, or when a portal asks for information that does not match the expected Delta flow. The fastest verification route is a flight attendant, not a guess based on signal strength or a polished login screen.
Delta says free Delta Sync Wi-Fi is available to SkyMiles members on most domestic and international flights, although service varies during the remaining aircraft rollout. That means a passenger may encounter different portals or service providers across connecting flights, making the airline’s preflight email and onboard instructions especially useful.
For travelers leaving a major convention city, the incident is also a reminder to separate local trip planning from the connection offered on the aircraft. Deep Arrival’s things to do in Las Vegas guide helps organize the city side of the trip, while a previous report explains how look-alike airport Wi-Fi networks can create the same basic identity problem on the ground.
What travelers should do if the network looks wrong
Do not enter a SkyMiles password, payment card, work login, or email credentials until the network and portal match Delta’s instructions. If the name is unfamiliar, disconnect, forget the network in device settings, and ask the crew which connection should appear.
If a traveler already entered a password into a suspicious portal, the next steps belong on the ground: change that password from a trusted connection, turn on two-factor authentication, review recent account activity, and avoid reusing the same password elsewhere. A company-managed device should also be reported to the employer’s security team.
Travelers should not attempt to locate or confront the person behind a network. Cabin crews and law enforcement have the authority and context to handle a report without creating a second safety problem in a confined aircraft.
It is also sensible to preserve details without spreading speculation. A screenshot of the network list, the approximate time, the flight number, and what the portal requested can help an airline investigate, while an accusation aimed at another passenger can easily be wrong.
What Delta has not established
No public statement reviewed for this report identifies a suspect, motive, device, or victim. There is also no confirmed finding that the network stole information, accessed the aircraft, interfered with navigation, or affected any system beyond the temporary shutdown of passenger internet.
The airline has not said whether Flight 591 landed late because of the response, whether a device was recovered, or whether federal authorities opened a formal case. Those are open questions, not gaps that can safely be filled with assumptions about hacking conferences or passenger intent.
The reported 30-minute interruption is nevertheless a meaningful operating consequence. It shows that even when aircraft safety is unaffected, a suspicious passenger-facing network can require the crew to remove legitimate connectivity while the situation is evaluated.
| If you see | What to do |
|---|---|
| DeltaWiFi.com and the expected Delta portal | Follow Delta’s published connection steps, then sign in or enroll through the official flow. |
| Two similar Delta network names | Do not choose by signal strength; ask a flight attendant which network is authorized. |
| A portal requesting unexpected credentials | Disconnect immediately and do not submit personal, work, or payment information. |
| A password already entered on a suspicious page | Change it from a trusted connection after landing and review the affected account. |
- Investigative finding: Delta has not identified who created the network or what the person intended.
- Federal role: The airline says it will coordinate with regulators and law enforcement, but no public case status is confirmed.
- Passenger impact: No affected account or data-loss report has been established publicly.
- Airline guidance: Watch for any change to Delta’s published network name or onboard connection sequence.
For now, the cleanest reading is narrow: Delta Flight 591 remained safe, the airline’s own network was not hacked, and the crew temporarily removed passenger Wi-Fi after a separate network appeared. The incident is serious enough to investigate without turning an unresolved onboard technology report into a claim of aircraft compromise.
Was Delta Flight 591 hacked?
Delta says no aircraft operating systems were affected and its legitimate in-flight network was not compromised. The airline is investigating a separate unauthorized Wi-Fi network.
How long was Wi-Fi unavailable on Flight 591?
The crew turned off the legitimate onboard Wi-Fi for about 30 minutes, according to Delta’s spokesperson.
What is Delta’s official onboard Wi-Fi network?
Delta tells passengers to select DeltaWiFi.com and open DeltaWiFi.com in a browser if the sign-in portal does not appear automatically.
Did a DEF CON attendee create the network?
That has not been established. The flight followed Las Vegas cybersecurity conferences, but no person, motive, or conference connection has been confirmed.